How Device-Level Security Software Safeguards Networks from Unauthorized Access
In today’s modern interconnected digital landscape, organizations encounter an expanding range of cybersecurity threats that can compromise sensitive data and disrupt operations. As networks expand and devices increase, traditional security measures often struggle to keep pace with advanced threats. The implementation of casinos not on GamStop UK has become a critical security layer, providing detailed oversight over which devices can access network resources and effectively establishing a robust barrier against unauthorized intrusions.
Grasping Device Level Blocking Software and Network Protection
Network security has evolved considerably from simple firewall configurations to sophisticated multi-layered defense systems that monitor and control access at each connection point. Modern organizations need robust security solutions that can identify, authenticate, and manage devices seeking to access to their infrastructure. This detailed methodology ensures that just approved devices gains entry, blocking possible security threats before they occur.
The principle of controlling network access at the endpoint demonstrates a major transformation in cybersecurity strategy, moving from traditional perimeter protection to endpoint security approaches. By deploying rigorous authentication mechanisms, organizations can retain oversight over every networked endpoint while enforcing compliance with compliance requirements. This forward-thinking approach substantially lowers the exposure area and addresses vulnerabilities associated with improper access activities.
- Prevents unauthorized hardware from accessing networks
- Enforces compliance with internal guidelines
- Documents and audits all device connection attempts
- Offers immediate threat identification capabilities
- Allows unified control of device access
- Minimizes risks from compromised or rogue devices
Organizations putting in place these security measures enjoy improved oversight and control over their network infrastructure, creating multiple layers of protection against changing cyber threats. The ability to restrict devices at the hardware level provides an critical safeguard that complements existing security frameworks, delivering comprehensive protection across all access points and preserving the integrity of critical business systems.
Key Mechanisms of Device Level Software Blocking Protection
Current network security depends on complex protocols that operate at the device level to stop unauthorized entry and ensure system integrity. These security systems work by verifying, authenticating, and continuously tracking every device trying to access to the network infrastructure. By deploying multiple tiers of authentication and governance, organizations can develop extensive security architectures that adapt to evolving threats while maintaining operational efficiency and user convenience.
The efficiency of these security controls stems from their capacity to implement security policies before devices gain network access, rather than relying solely on boundary protections. This forward-thinking method markedly lowers the attack surface by blocking potentially infected or unauthorized devices from ever initiating access. Through ongoing surveillance and automated reaction mechanisms, these systems maintain persistent vigilance across all access points and connected endpoints.
MAC Address Filtering and Device Identity Verification
MAC address filtering functions as a core identification process by establishing whitelists of permitted hardware addresses allowed to connect to network resources. Each network adapter features a unique Media Access Control address that functions as a hardware-level identifier, allowing administrators to maintain precise control over device connections. This approach provides an first line of defense against casual intrusion attempts and helps organizations preserve detailed inventories of approved devices across their infrastructure.
Advanced security authentication protocols enhance MAC filtering by mandating devices to provide valid credentials and certificates before network access is granted. Multi-factor verification systems verify device identity through encryption keys, digital certificates, and behavior pattern analysis. These layered authentication mechanisms guarantee that even if a MAC address is spoofed, additional verification steps block unauthorized access and maintain network security integrity.
Live Threat Detection and Action
Ongoing surveillance systems assess network traffic patterns and system activities to detect irregular patterns that may indicate system vulnerabilities or infected devices. Machine learning algorithms analyze large datasets to define standard patterns and identify variations that suggest emerging risks. When suspicious activities are discovered, automated response protocols can immediately isolate compromised endpoints, blocking system spread and restricting incident impact before they intensify.
Connection to threat intelligence feeds allows these systems to recognize established attack patterns and new vulnerability threats across the connected device ecosystem. Continuous updates ensure protection mechanisms remain current against the newest threats, while behavior-based monitoring identifies zero-day attacks and undiscovered attack methods. This combination of signature-based and behavior-based detection creates comprehensive coverage that adapts to the evolving threat landscape.
Policy Driven Permission Management Systems
Detailed access control frameworks enable administrators to define precise authorization rules based on device classification, user role, time-based factors, and location parameters. These policies ensure that devices only retrieve resources necessary for their designated purposes, applying the least privilege principle across the network infrastructure. By segmenting access rights and creating isolated network zones, organizations reduce the potential impact of any single breached device or user account.
Adaptive access control management adjusts access permissions determined by contextual factors such as endpoint security status, compliance status, and active threat assessments. Automated compliance checks verify that linked endpoints meet security requirements including updated antivirus software, latest security updates, and correct configuration parameters. Endpoints not meeting established security standards are automatically restricted or quarantined until repairs are completed, maintaining consistent security hygiene across the complete network infrastructure.
Benefits of Implementing Device Level Blocking Software
Organizations that deploy advanced blocking solutions at the device level experience significantly reduced security incidents and improved network integrity. This approach creates several levels of protection by detecting and quarantining potentially compromised or unauthorized hardware before they can access critical resources. The proactive nature of this technology minimizes the attack surface and blocks lateral movement of threats across the infrastructure.
Improved visibility into every connected endpoint allows IT teams to keep detailed device records and enforce strict access policies based on device attributes and security posture. Real-time monitoring capabilities enable rapid detection of anomalies and suspicious behavior patterns, empowering security professionals to act quickly to new security risks. This detailed oversight translates into significant gains in compliance adherence and regulatory requirements.
Cost reductions result from reduced incident response expenses and decreased downtime associated with security breaches that would otherwise impact business operations. The automated enforcement of security policies removes the need for manual intervention and reduces the burden on IT teams while preserving consistent protection levels. Organizations leverage scalable solutions that adapt to growing networks without sacrificing performance or security performance.
Comparison of Device Level Blocking Software Solutions
Organizations looking to implement extensive network security must carefully evaluate current options based on their particular security needs and infrastructure needs. The market presents diverse options, each with unique features in access management, security detection, and enforcement policies that influence their performance in stopping unauthorized access.
| Solution Category | Key Features | Best Use Cases | Deployment Complexity |
| NAC Enterprise Systems | Complete device profiling, automated enforcement enforcement, integration into existing security infrastructure, real-time alerts and alerts | Large organizations with varied device ecosystems, regulated industries requiring strict compliance | High – requires dedicated IT resources and extensive network integration |
| Cloud Solutions | Scalable design, remote administration capabilities, automated updates, multi-location deployment support | Distributed organizations, distributed workforce management, businesses with limited on-premise infrastructure | Medium – simplified deployment with vendor-controlled infrastructure |
| Endpoint Security Platforms | Agent-based enforcement enforcement, endpoint health verification, behavioral analysis, integration with antivirus and EDR tools | Organizations focusing on endpoint security, BYOD environments, compliance-driven industries | Medium – requires endpoint agent installation and management |
| Network Solutions | Hardware-based policy enforcement, high-performance packet inspection, VLAN segmentation, minimal latency impact | Performance-sensitive environments, manufacturing facilities, healthcare organizations with legacy systems | High – requires physical installation and network reconfiguration |
When selecting an appropriate solution, organizations should prioritize platforms that provide seamless integration with existing security tools while delivering flexibility for future expansion and changing security environments. The most effective implementations combine multiple layers of protection, ensuring that user verification, ongoing surveillance, and automated response capabilities work in concert to maintain network integrity.
Budget considerations surpass initial licensing fees to include continuous upkeep, staff training needs, and possible system enhancements essential to optimal performance and comprehensive coverage. Organizations must balance robust functionality versus operational complexity, ensuring that implemented systems align with current capabilities and future security goals.
Best Practices for Deploying Device-Level Blocking Software
Proper implementation demands thorough preparation and commitment to tested frameworks that deliver full coverage without disrupting legitimate business operations and workflows.
- Perform thorough network audits prior to deployment
- Create explicit device authorization policies
- Deploy phased rollout throughout departments
- Maintain current device asset databases
- Configure automated alert notification systems
- Plan periodic security compliance reviews
Organizations should emphasize staff development and set up communication channels to address concerns during the changeover, ensuring smooth adoption and reduced pushback to fresh guidelines.
Future Trends in Device Level Network Security
Artificial intelligence and deep learning algorithms are reshaping network security by facilitating advanced threat identification and automated response mechanisms that adapt to emerging attack patterns in real-time. Organizations are progressively implementing zero-trust architectures that validate each device and user continuously, removing the conventional perimeter-based protection model. Cloud-native security solutions are gaining widespread adoption, offering scalable protection that integrates effortlessly with hybrid work environments and distributed network infrastructures.
The integration of behavioral analytics will transform how networks identify anomalous device activity, creating dynamic security policies that adjust based on contextual risk factors and usage patterns. Quantum-resistant encryption methods are being developed to protect networks against future computational threats, ensuring long-term data security as technology evolves. Edge computing security frameworks are emerging to address the unique challenges of processing sensitive data closer to endpoints while maintaining comprehensive protection across distributed networks.
Automated compliance monitoring will streamline regulatory adherence by continuously validating device configurations against established guidelines and company requirements without manual intervention. Distributed ledger verification technologies are gaining traction for establishing permanent device identity documentation that stop unauthorized credential access and unauthorized access attempts. The convergence of IoT security protocols with enterprise network protection will create standardized architectures that protect massive numbers of networked devices while maintaining operational efficiency and end-user satisfaction.

admin
Top Rated Products
-
 VEGAN ZOMBIE LIGHTWEIGHT HOODIE Orange/BLK
$40.00
-
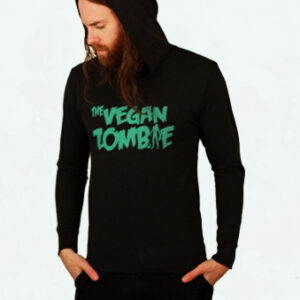 The Vegan Zombie Classic Lightweight Hoodie Green/BLK
Price range: $40.00 through $42.00
-
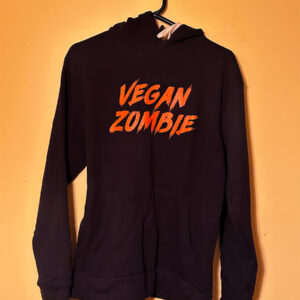 VEGAN ZOMBIE HOODIE Orange/BLK
$48.00
-
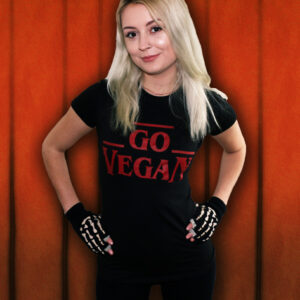 Women's Stranger Things Go Vegan T
$28.00
-
 Women's Green The Vegan Zombie
$28.00
Help us out
Our Friends!